Featured

Rice Tea Cat Panda CTF Writeup

Challenge: [What’s the Password: Revisited] (Reverse Engineering)
Author: DarkEnigma

First, I drop the file into exeinfoPE to see some information
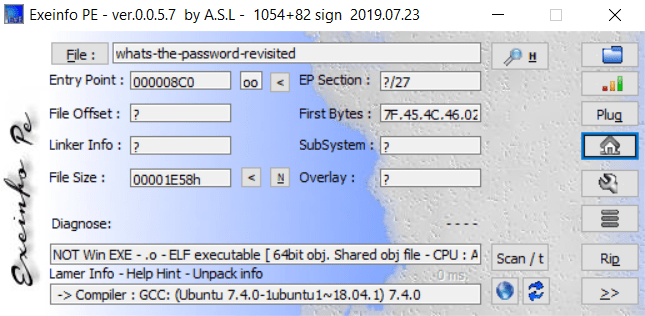
And you can see it’s an ELF64 for x86-64 structures, now i’ll analyse it by using IDA Pro and decomplie it from funcion Main.
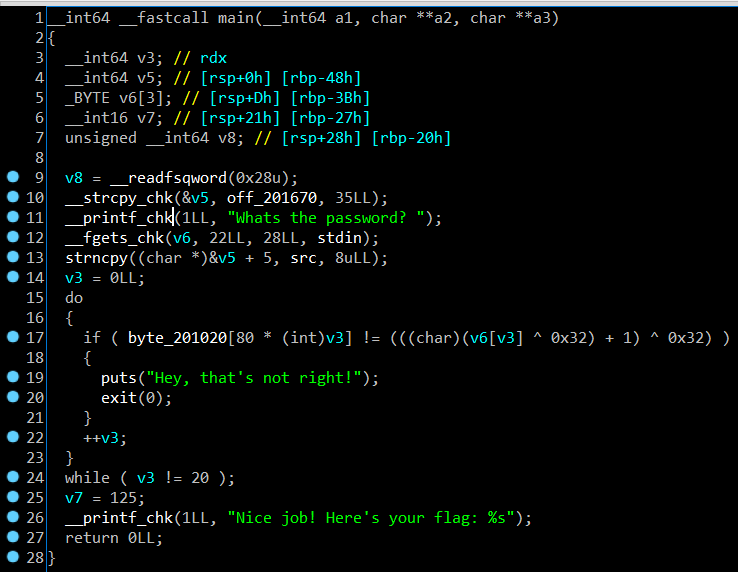
OK, i saw loop at line 15 to 24, you’ll see a conditional v3 != 20 it mean the length of password, so I started at line 10 and see off_201670 in a strcpy command, the off_201670 is returned result “rtcp{” and store in v5 variable . Then, in line 13 i see strncpy((char *)&v5 + 5, src, 8uLL), it mean it’ll copied v5 and src has 8 characters, the src i found it in IDA at address 0x201668 and 0x201670
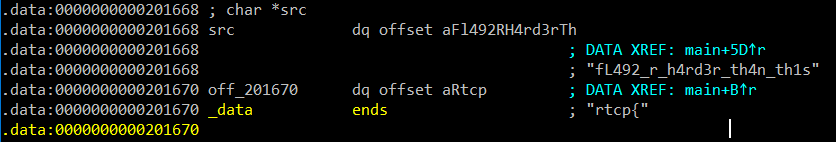
So, i easy found the flag from the scrncpy command which is: “rtcp{fL492_r_” :), next i continue to see conditional at line 17:

v3 = 0LL;
do
{
if ( byte_201020[80 * (int)v3] != (((char)(v6[v3] ^ 0x32) + 1) ^ 0x32))
{
puts("Hey, that's not right!");
exit(0);
}
++v3;
}
while ( v3 != 20 );

This conditional has algorithm XOR and i see byte_201020 elements at 0x201020
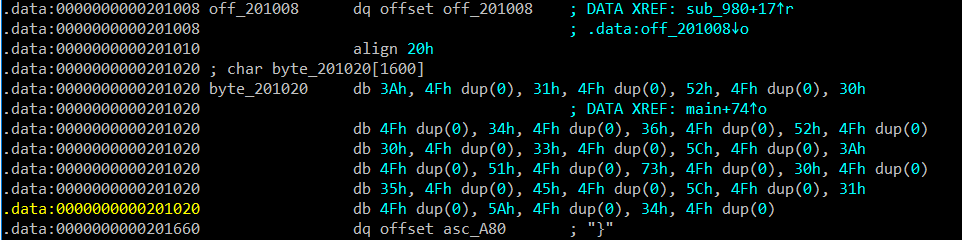
You can see the elements with the max size is 0x4F so i collects value: 0x3A, 0x31, 0x52, 0x30, 0x34, 0x36, 0x52, 0x30, 0x33, 0x5C, 0x3A, 0x51, 0x73, 0x30, 0x35, 0x45, 0x5C, 0x31, 0x5A, 0x34 and i coded it by python

After run it, we have the flag: rtcp{fL492_r_50m371m32_5Pr34D_0U7}

——————————– THANKS FOR WATCHING ——————————–

Featured

NoobTeaM CTF Writeup

Challenge: CrackOs (Reversing)

Đầu tiên, tôi sẽ tiến hành kiểm tra sơ về file crackos.exe:

CrackOs.exe 🙂

Tiếp theo tôi sẽ dùng IDA để tiến hành phân tích file này và chúng ta sẽ xem nó ở hàm main và tiến hành tìm các ký tự ở strings windows

Trong chall này tôi sẽ đưa ra ý tưởng từ strings windows đó là đi tìm serial key, có 2 hướng để tìm: 1 bạn hãy xem toàn bộ trên Graph Overview và hãy để ý thật kỹ các hàm cmp xuất các ký tự hoặc dễ hơn là decomplie trên ida, ở đây tôi sẽ dùng cách 2 nhé 🙂

Tiến hành Decomplie ở hàm main.

Tôi sẽ bắt đầu bằng việc tìm độ dài của flag:

if ( strlen(&Dst) <= 0x18 )
salida();

Điều đó cho thấy độ dài ký tự phải trên 24 nếu không nó sẽ báo lỗi và thoát chương trình :(, sau đó tôi sẽ tiếp tục tìm ký tự đầu và ký tự cuối thông qua các biến, bạn hãy quan sát hàm dưới đây:

if ( Dst != v25 )
salida();

Nó có liên quan tới hàm kiểm tra strlen trên, như vậy tôi có thể biết được ký tự đầu tiên bắt đầu bằng giá trị ở biến v25 , tiếp tục kiểm tra xem giá trị của nó là bao nhiêu:

if ( v25 != v36 )
salida();
if ( v36 != 78 )
salida();

Như vậy chúng ta biết được ký tự đầu có giá trị là 78, chuyển sang ký tự nó là ‘N’, đến đây bạn có thể tiếp tục tìm hết từ đoạn Dst –> v39 và biết được chính xác độ dài ký tự bằng 25. Chuyển hết sang dạng ký tự ta sẽ tìm được serial key, ở đây tôi viết code để chuyển từ Dec sang text luôn 🙂
Các bạn có thể tải file ở đây: https://drive.google.com/file/d/1bhV9GhDkxYxf2BpZBQCAS_4Tb4K96iXt/view

  • OK !!!, tôi đã tìm ra được serial key: Nzey7-drFLN-ctfgH5-puNF6Y

Cho chạy trên cmd, ta sẽ tìm thấy flag 🙂

Như vậy kết thúc việc giải chall crackos ở đây, nếu có thắc mắc hãy liên hệ mình qua Facebook: https://www.facebook.com/Th3Sea001, thanks for watching

b01lersCTF bootcamp

Last night, i and my friend played b01lers CTF and got a 1st in VietNam :V, i solved some rev in this ctf. After i finish the most tasks, i think this ctf is for beginner but some tasks i think it so fun, now let’s start !!!

Solved:
Link Battle 
Mega Race
Thumb Thumb
Welcome To Game Over
Goat

Link Battle

This file is an ELF library, so you cannot run it, load in IDA, we have:

if a1 != 6666 is the password to get flag, you can write a script to print result, the best way to solve it is use ctypes to call getflag function, here’s my solution :v

and……. :v :v :v

Goat

This’s a small Java crackme :v, in this challenge there’s 4 part of 4 loops in Crackme function, so in functions, you have to watch and ask your self: which loop need to be reversed ?, then in 4th loop, this is a random-seed + xor encryption, you can use java in their chall to calc the seed :V, here’s my solution example:

after you found the seeds, let’s go to the finish :v :v :v

oh, it ended :v. Anyway, thanks for watching my blog 😉

~ WPICTF 2020 ~

Challenge: NotWannasigh – 100 pts [Reversing]

Solution: Find the key from file .pcap – a seed random simple, then you use xor to decrypt the file to get a flag, the flag is gif file 🙂

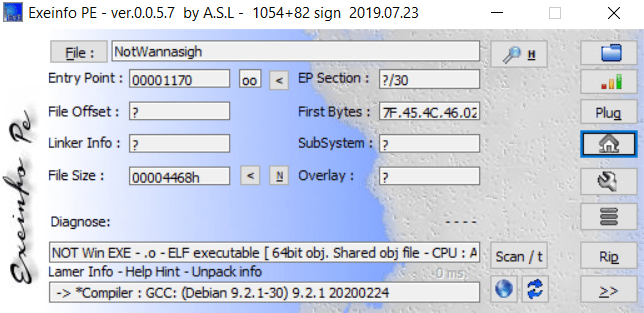
OK, an ELF 64 bit execuable, nothing special (~.~), start analyze it by IDA:

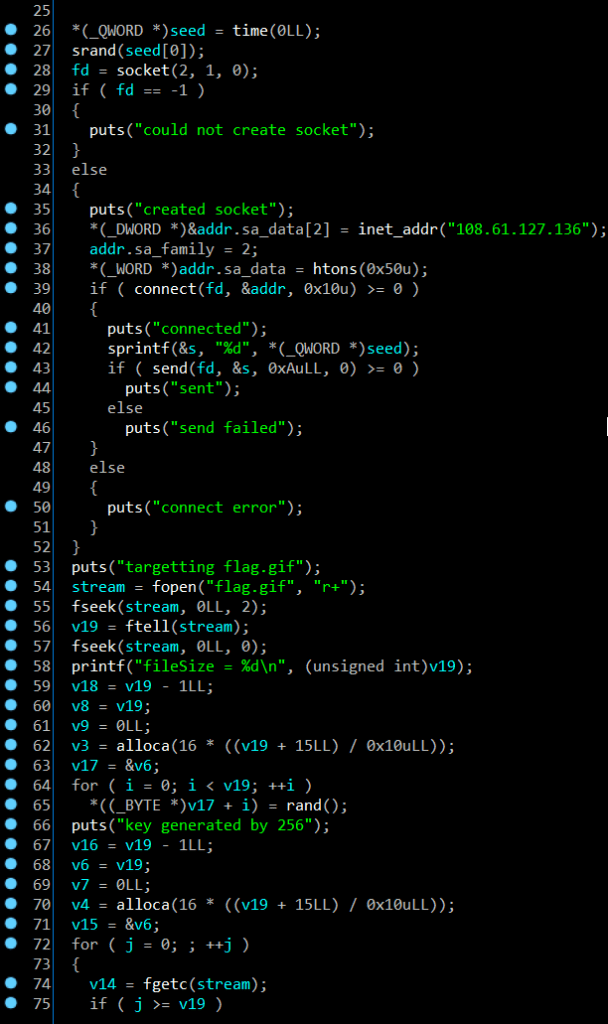
Main Function

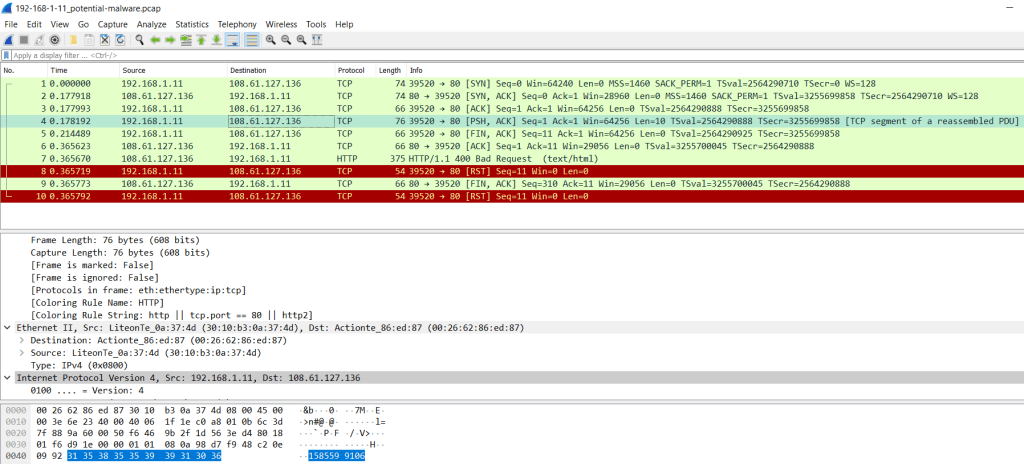
This func told me that encrypted file flag.gif to flag-gif.enciphered by XOR with key and the key we known that from this seed in file .pcap. Using Wireshark to analyse it:

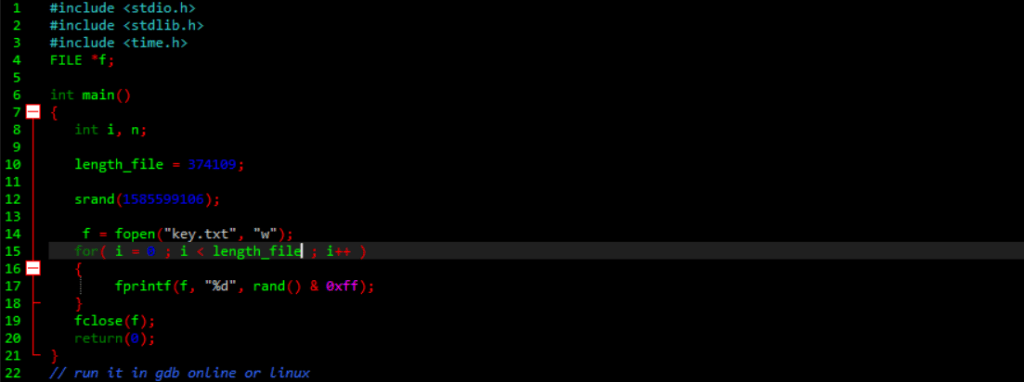
We can see the sockets was created by “Malware” to connect the server, so the seed will be printed after connected successful and we got 1585599106 is the seed that we need, then we know the length of .pcap file is same than the keys, you can check the length by using print(len(something)), let’s do it !!!

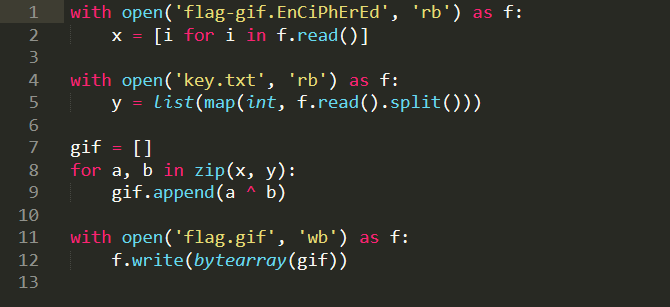
The key has 8 bits so rand() should be AND with 0xff and run it in linux because it work better than windows. After we got the keys, we’ll xor it to decrypt the file

After run it, we got the gif file !!!

UTCTF Writeups

[Reverse Engineering] by DarkEnigma

Challenge 1: [basic] reverse engineering (50 pts)
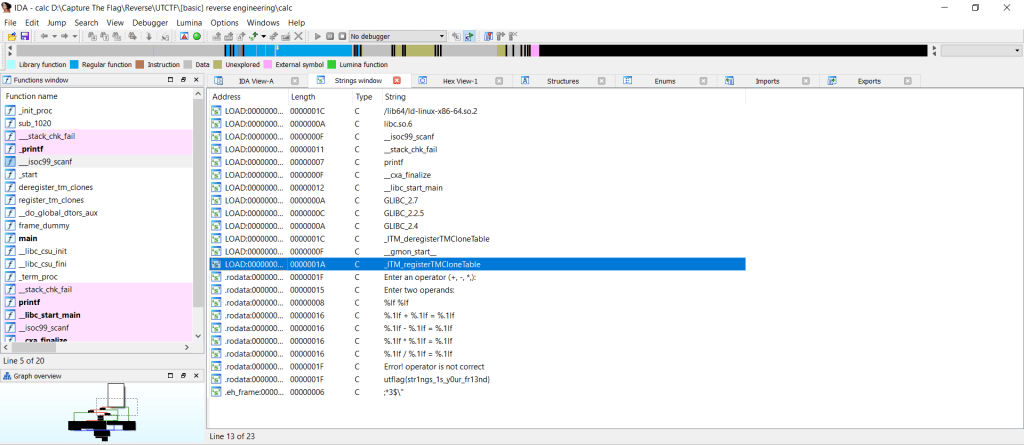
Solution: just find a flag in strings window 🙂

flag: utflag{str1ngs_1s_y0ur_fr13nd}

Challenge 2: babymips (50 pts)
Solution: I using Ghidra to see assembly easier 😉
XOR algorithm to get a flag

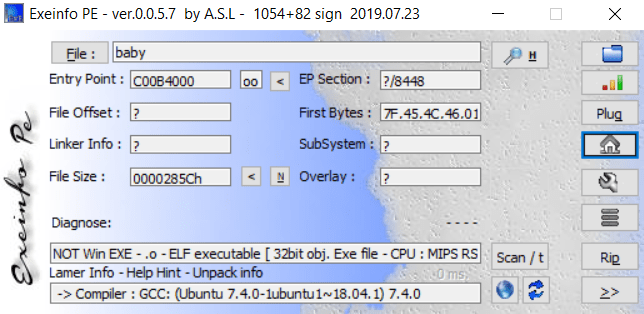
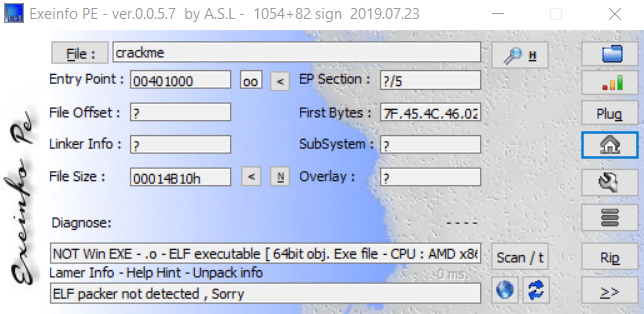
First i using exeinfoPE to view some information:

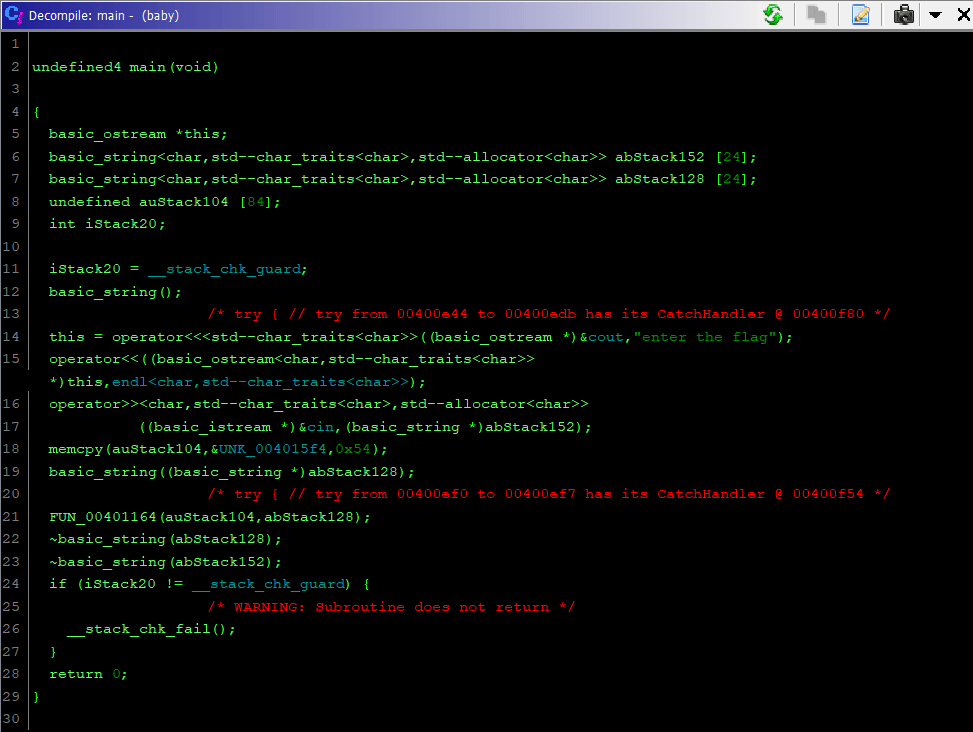
~ OK, a 32bit of ELF execuable file, now we strarting analysis main() function.

OK !!!, i have a maximum characters is 84 from memcpy command and i get an encrypted flag UNK_004015f4 but i don’t know the real length flag so i continue follow funciton FUN_00401164 in line 21:

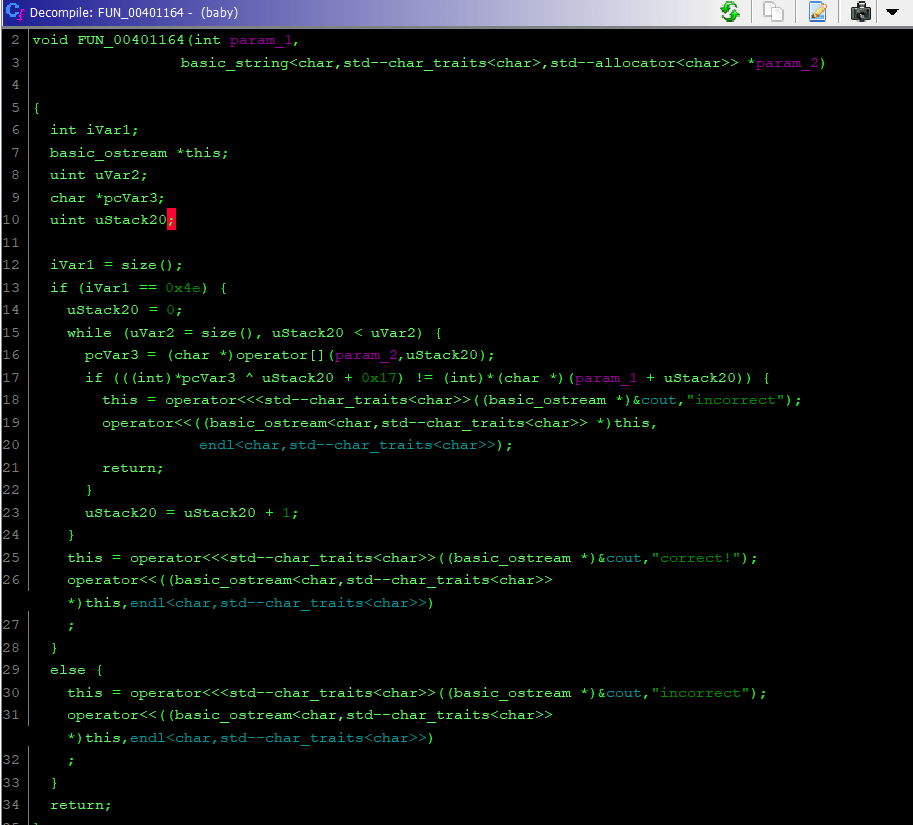
ARGIHT !!!, we can see in line 13: if(iVar1 == 0x4e), so we know the length of flag is 78 (0x4e) and bonus an encrypted flag in main() we have: 0x62, 0x6c, 0x7f, 0x76, 0x7a, 0x7b, 0x66, 0x73, 0x76, 0x50, 0x52, 0x7d,0x40, 0x54, 0x55, 0x79, 0x40, 0x49, 0x47, 0x4d, 0x74, 0x19, 0x7b, 0x6a,0x42, 0xa, 0x4f, 0x52, 0x7d, 0x69, 0x4f, 0x53, 0xc,0x64, 0x10, 0xf,0x1e, 0x4a, 0x67, 0x3, 0x7c, 0x67, 0x2, 0x6a, 0x31, 0x67, 0x61, 0x37,0x7a, 0x62, 0x2c, 0x2c, 0xf, 0x6e, 0x17, 0, 0x16, 0xf, 0x16, 0xa, 0x6d,0x62, 0x73, 0x25, 0x39, 0x76, 0x2e, 0x1c, 0x63, 0x78, 0x2b, 0x74, 0x32,0x16, 0x20, 0x22, 0x44, 0x19

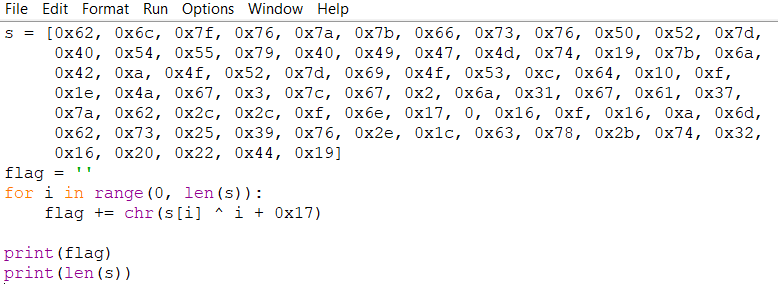
Continue in line 17: a simple XOR so we can get a flag by python:

🙂 Finally we got the flag: utflag{mips_cpp_gang_5VDm:~`N]ze;)5%vZ=C'C(r#$q=efD"ZNY_GX>6&sn.wF8$vmvA@'}

Challenge 3: Crack The Heart (1411 pts) 🙂
Solution: using Debugger skill 🙂
~~ i spend 2 days to solve it 😦 ~~

Lucky this file is ELF 64 bit execuable !!!

Because this challenge is too long so i can tell you some ways to get a flag:
– First you must debug it so view this asm code !!
– after debug you’ll see a simple anti-debug so you must bypass it to see more asm code
– set breakpoint your input and get all values in bl registers and al registers, expect bl you must trace 1 loop to see the next value on bl registers, all the values of al, bl you can see it in command xor bl, al
– you can find values of al registers in address 0x402137
*note: you just see asm code while debugging 😉

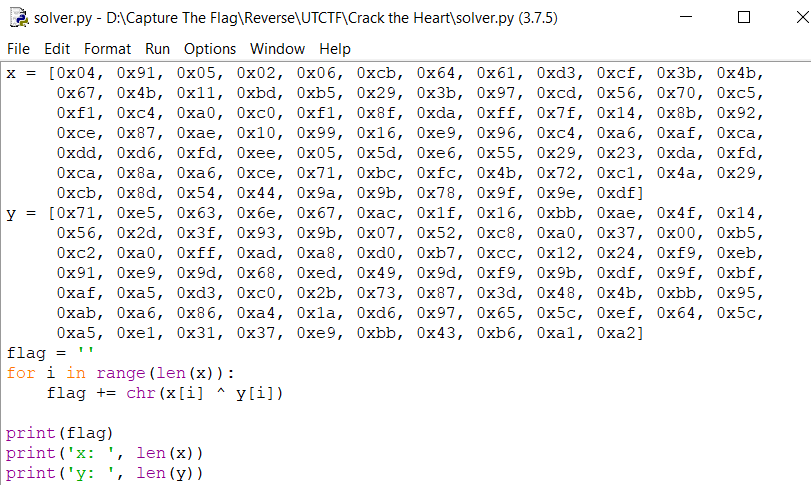
after that you can get a flag by using python:

flag: utflag{what_1f….i_mapp3d_mY_m3m0ry_n3xt_to_y0urs….ahahaha, jkjk….unless ;)?}

i know somebody didn’t understand what i said so you can contact me in telegram: t.me/Th3Sea001

Anyway, this challenge reversing so interesting, thank you UTCTF ❤

Tic Tac Toe – Batamlinux CTF Writeup

link challenge: http://ctf.batamlinux.com/challenges#Tic%20Tac%20Toe (Reverse Engineering)

First i need information of tictactoe so i used exeinfoPE

Solution: I found a “big” bug in this file could be shown a flag without playing a minigame :). It’s true ?, YES !!!, a flag contained in function mem(), now I’ll analysis all function in TicTacToe

Main()
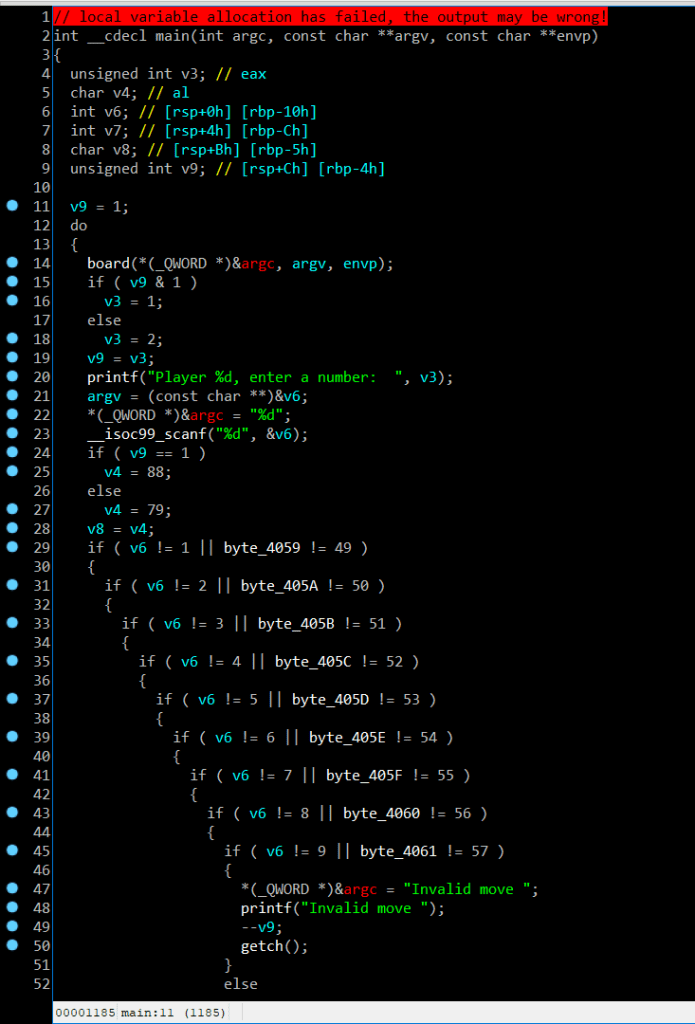
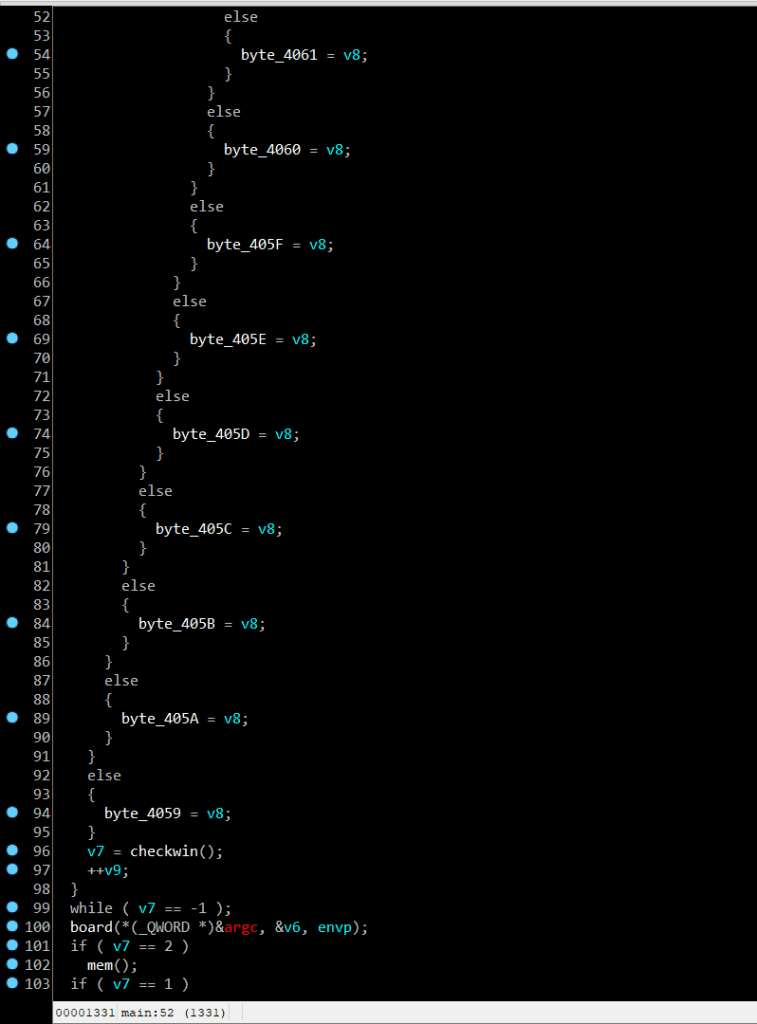
TicTacToe is a carogame (3×3) has 2 players, if player 1 or 2 write 3 X (O) continuity, they’ll win, so in func main() i decompile it to analyse:

In line 29 ->45 are checked if correct move, go to func checkwin() and if right, it’ll be return 2 and unless, it’ll return 1. So mem() function is contain a flag, but unfortunally this file cannot run without file libncurses.so.6,…..so sad but that’s OK, let’s analysis this func !!!

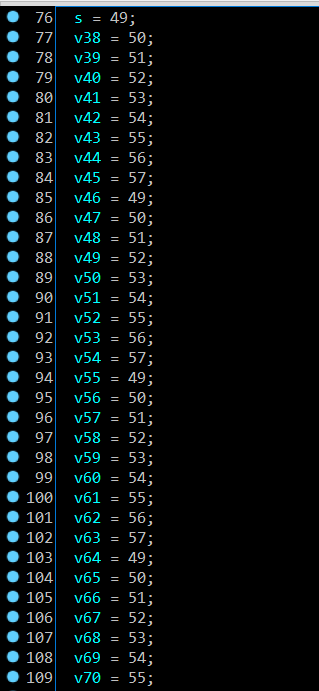
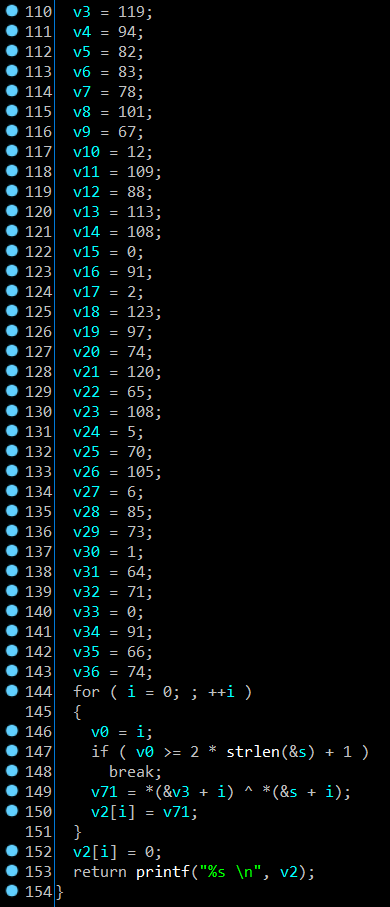
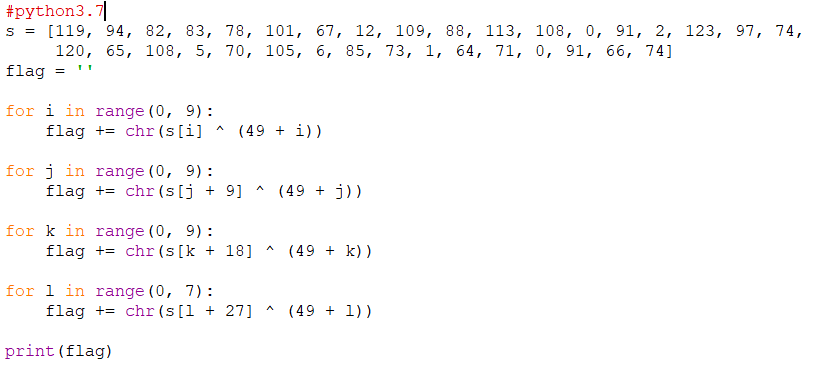
Here we are, an encrypted flag with using XOR algorithm in line 149, did you think a length password is 68 (from s to v70) ?. No, that’s not right because you saw line 149, there was v3 variable xor s variable. It mean divided into 2 parts: v3 (v3 –> v36) and s (s –> v70), when i checked length, the answer is 34 and did you see some number in array S (i called it) is 49, 50, 51, 52,…57 and continue loop ? This is a big problem which i want to tell you, let me describe it: when you use loop while used xor algorithm, (49 + i) will be ascended to 57, if (49 + i) or you can understand (&s + i) > 57, it’ll return back.To more describle it, i’ll code by python:

after you run this, you’ll get the flag 🙂

anyway, this challenge so interesting, i spent much time to solve it. Maybe i’ll stop this writeup, if you don’t understand about this challenge, here is my telegram: https://t.me/Th3Sea001

—————— THANKS FOR WATCHING ——————–

Design a site like this with WordPress.com
Get started